


 USD

Bitget Raises Security Breach Estimate to $387.5M After Multi-Chain Attack

Exchange traces additional Zcash and TRON assets as recovery effort expands
TL;DR
- Bitget raised the confirmed value of assets transferred to attacker-controlled addresses to about $387.5 million after identifying additional Zcash and TRON transactions.
- Arkham Intelligence traced roughly $350 million across seven blockchains, including a $228 million outflow compressed into an 18-minute period.
- Bitget launched a 5% recovery bounty while withdrawals remained paused and Mandiant and SlowMist continued the investigation.
Trade smarter on Jupiter, Solana’s leading DEX built for fast execution and deep liquidity.
Swap tokens at competitive rates, route across multiple liquidity sources automatically, and access perpetuals, DCA, and advanced trading tools — all in one place!
Bitget said on September 25, 2026, that approximately $387.5 million in assets had been transferred to attacker-controlled addresses during its September 24 security incident, raising its earlier estimate after additional Zcash and TRON transfers were identified. The exchange said the higher figure reflected a fuller accounting of the original breach rather than new unauthorized transfers, and said the incident had been contained.
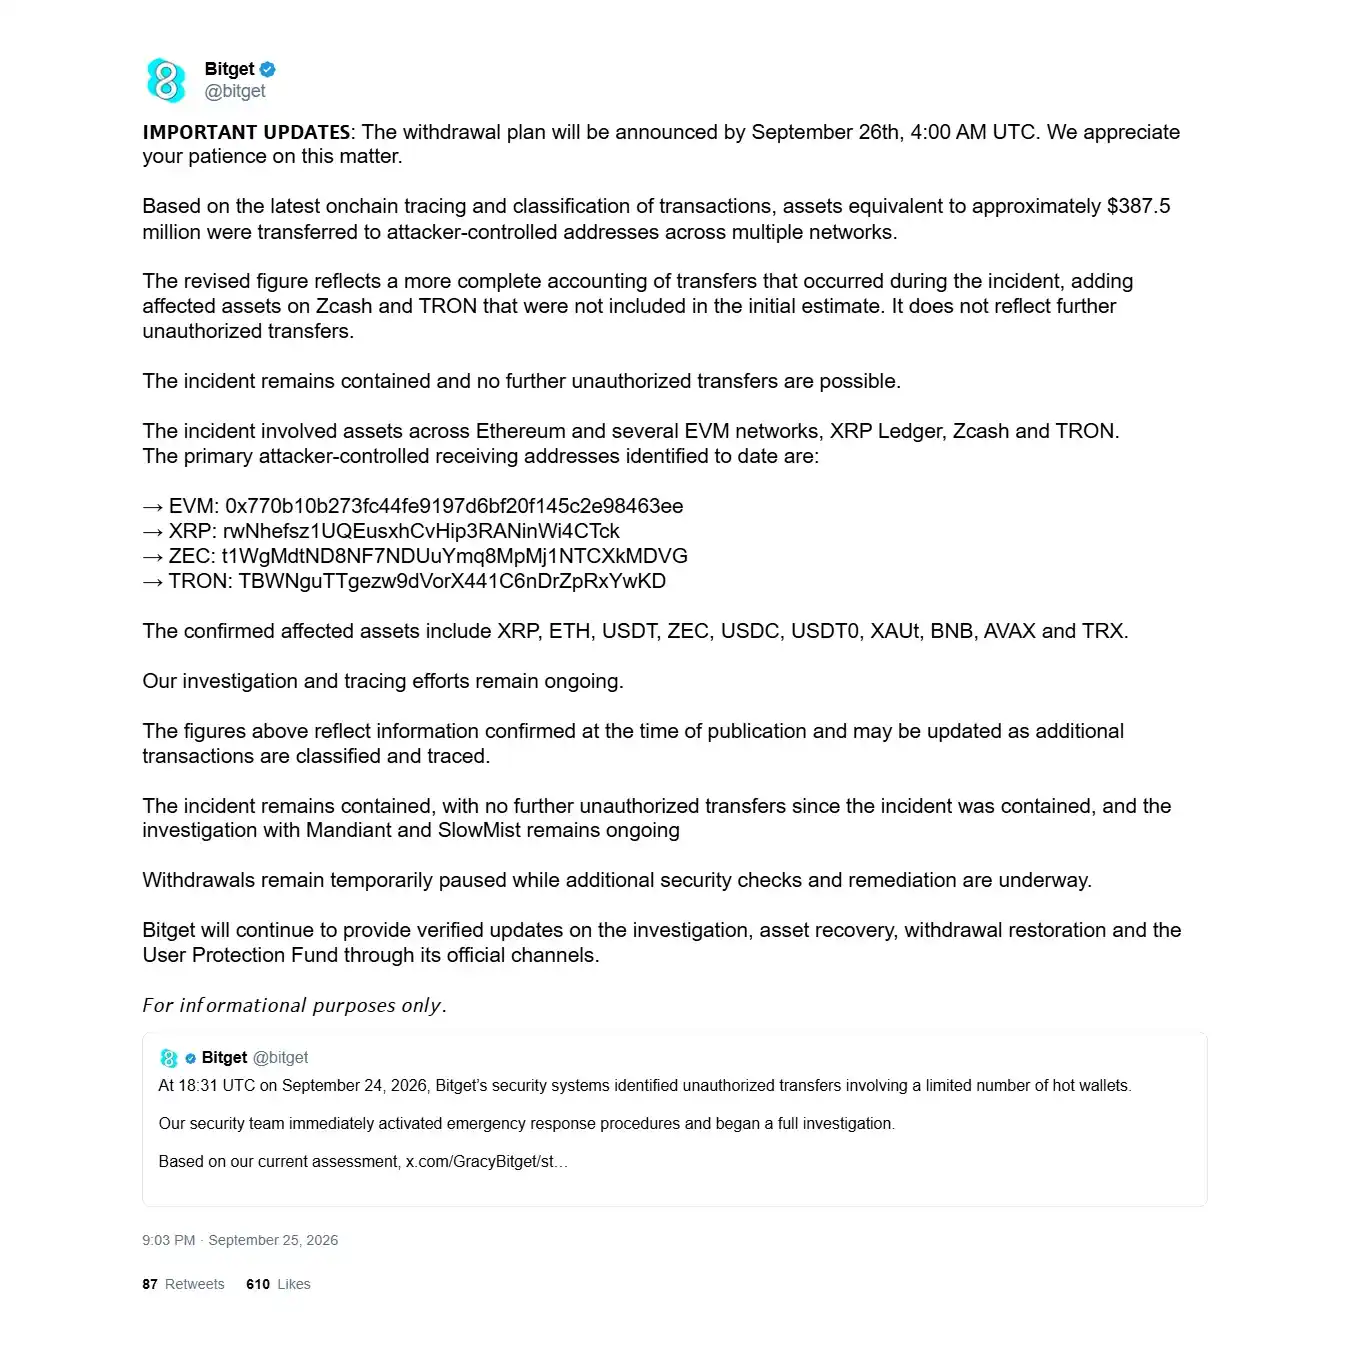
Bitget had initially estimated affected assets at $351.6 million. The revised total represented an increase of about $35.9 million, or roughly 10.2%. Bitget said the change resulted from “a more complete accounting of transfers that occurred during the incident” and did not reflect another round of theft. The company said no further unauthorized transfers had occurred after containment and that the underlying vulnerability had been fixed.
Bitget CEO Gracy Chen said the security team identified the attack path and how the attacker bypassed existing controls. Chen described the incident as a compromise of a backend system in Bitget’s wallet infrastructure, where attackers spoofed transaction data and triggered the authorization process to move assets. She said the event did not result from a private-key compromise.
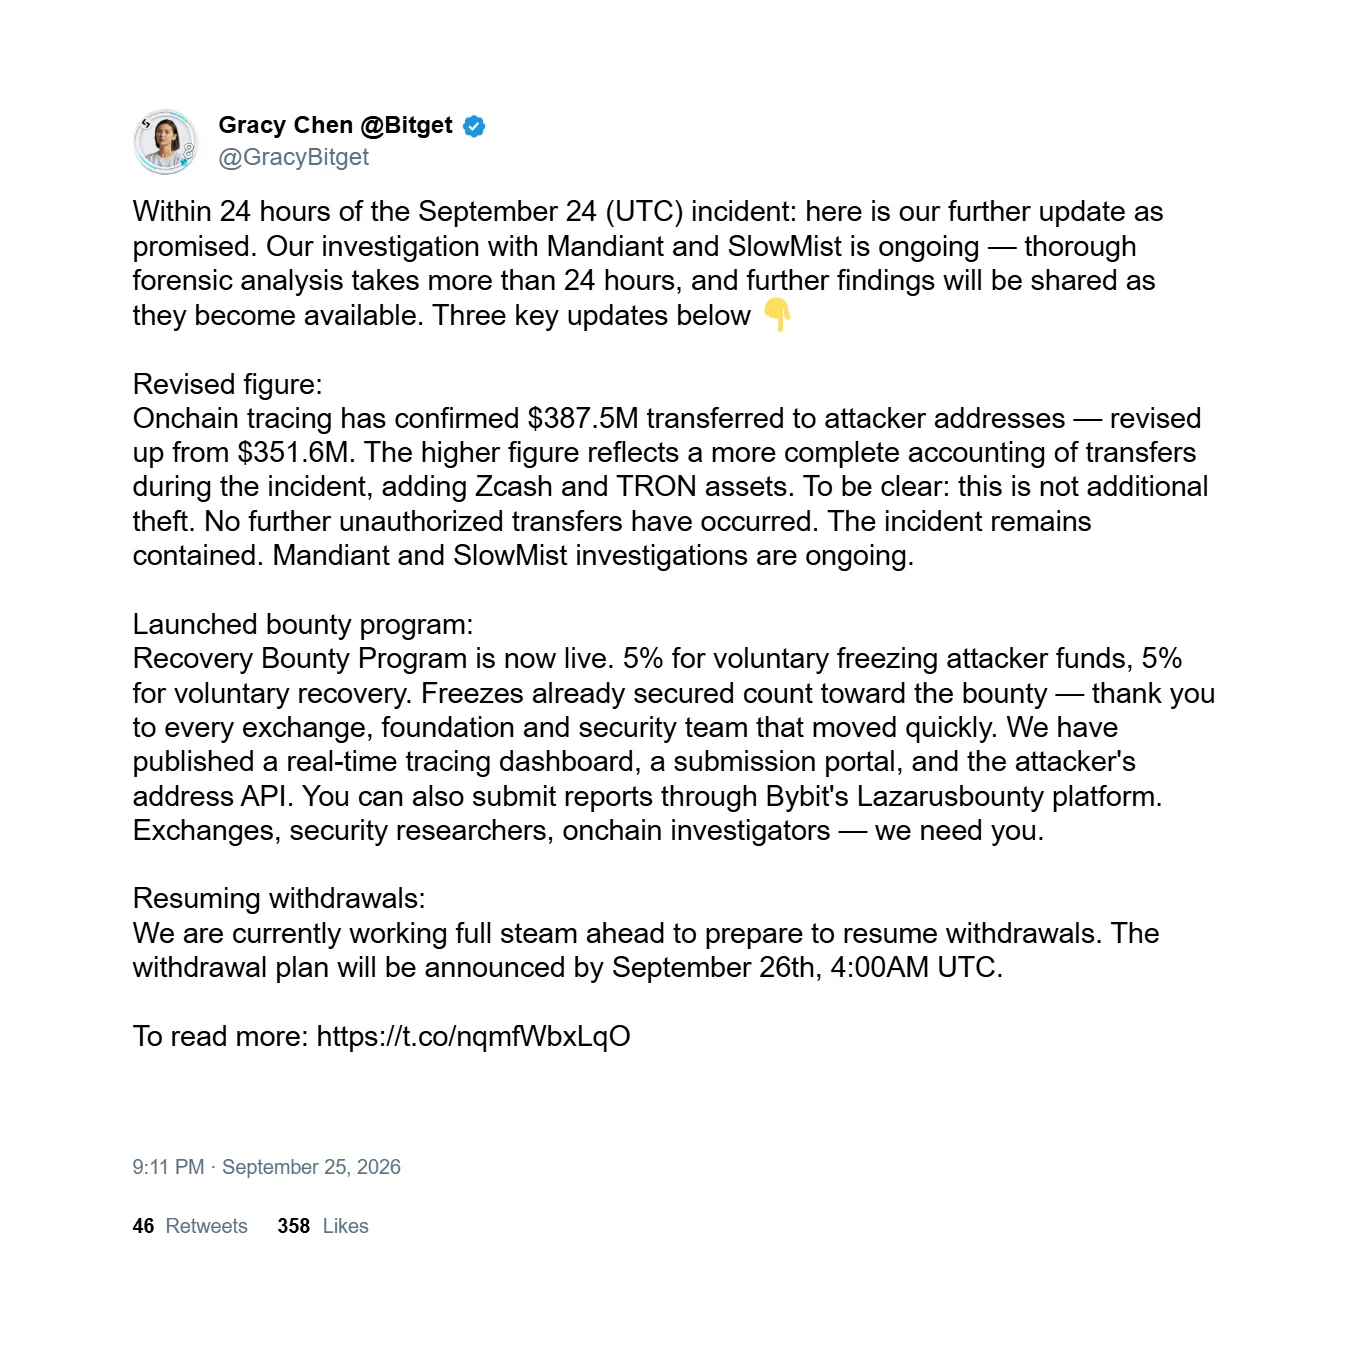
Mandiant and SlowMist continued working on the investigation and forensic review. Chen said, “thorough forensic analysis takes more than 24 hours, and further findings will be shared as they become available.” Bitget said additional security checks and remediation work were continuing even after the immediate vulnerability had been addressed.
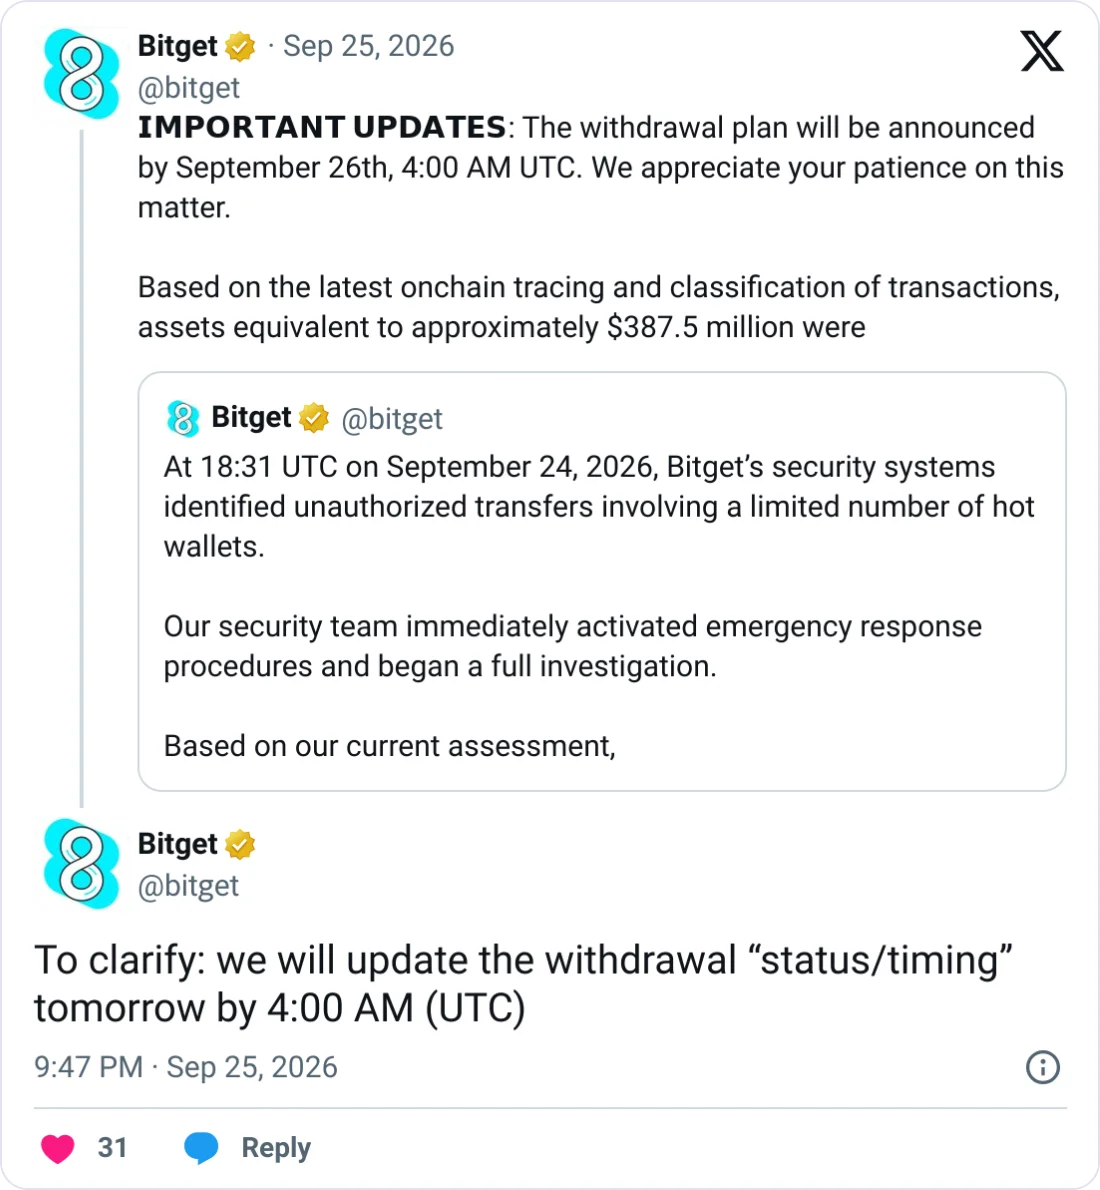
Withdrawals remained temporarily paused. Bitget said deposits and trading had remained available earlier in the incident response and planned to provide an update on withdrawal “status/timing” by September 26 at 4:00 AM UTC, rather than guaranteeing that all withdrawal functions would necessarily resume at that moment.
Attack Spread Across Multiple Networks
Bitget said the incident affected Ethereum and several EVM networks, XRP Ledger, Zcash and TRON. Confirmed affected assets included XRP, ETH, USDT, ZEC, USDC, USDT0, XAUt, BNB, AVAX and TRX.
Bitget identified four primary attacker-controlled receiving addresses:
Arkham Intelligence separately traced roughly $350 million leaving five Bitget wallets across seven blockchains — XRP Ledger, Ethereum, Arbitrum, Optimism, BNB Chain, Avalanche and Base — between about 2:31 p.m. and 5:23 p.m. EDT during the attack. Arkham said, “Of the $350M, $228M left Bitget in 18 minutes, from 18:58 to 19:16 UTC.” That burst represented roughly 65% of the amount Arkham traced.
Arkham had labeled 26 addresses linked to the attackers by the time of its postmortem. Its attacker portfolio showed approximately 68,466 ETH worth about $185.13 million, excluding stolen XRP held separately on XRP Ledger addresses.
XRP was the largest single identified component in Arkham’s breakdown at approximately $153 million. About 103 million XRP were involved, and more than 99% remained in five XRP Ledger addresses early the next day. Arkham characterized the XRP source as a Bitget cold wallet, while Bitget said its cold wallets remained secure and that affected funds came from portions of its hot and warm wallet infrastructure. The two accounts therefore differed over the wallet classification.
Early estimates had focused on approximately $174 million to $183 million moving from Bitget-labeled wallets before investigators traced additional transfers. Those figures increased as more chains, wallets and assets were classified.
Attackers Swapped, Bridged and Split Stolen Assets
Arkham said the attackers began selling stablecoins and tokenized gold for ETH within about 10 minutes of the theft. Approximately $25 million in USDT was sent to Rizzolver through five separate $5 million transactions, while additional swaps were routed through Uniswap, 1inch and Furucombo.
USDC was moved to Ethereum before being sold, while assets from Arbitrum, Optimism and Base were also bridged into Ethereum. Arkham said that bridging activity had been completed by approximately 4:04 p.m. EDT.
Arkham estimated that about $100 million of stolen assets other than ETH were converted into roughly 36,600 ETH. The attackers later split ETH across newly created wallets. Eight addresses held approximately 68,300 ETH worth around $183 million at the time of Arkham’s analysis, with no outgoing transactions observed from those wallets at that point.
BNB Chain funds remained active. Arkham traced approximately $6.9 million to 12 unlabeled BNB Chain wallets, including at least $4.7 million sent to THORChain and another $2 million deposited into FixedFloat. Arkham noted that THORChain had appeared in an unrelated investigation of stolen crypto funds but said that prior use did not establish who conducted the Bitget attack.
Circle and Tether Freeze Part of the Stolen Funds
Circle blacklisted an Ethereum address labeled “Bitget Exploiter 8” at approximately 05:00 UTC the following day. The wallet held about 170.47 ETH, 218,023 USDT and 99,990 USDC. MistTrack said Tether later banned the same wallet.
The USDT and USDC balances represented approximately $318,000 in frozen stablecoins, or about 0.08% of Bitget’s revised incident amount. MistTrack said other exploit-linked wallets still held more than 63,000 ETH.
Bitget said some industry partners had already frozen affected assets and urged stablecoin issuers, exchanges, bridges, custodians, blockchain projects and other infrastructure providers to monitor attacker addresses and report relevant activity.
Bitget Offers 5% Recovery Bounty
Bitget launched a Recovery Bounty Program offering 5% of funds successfully frozen to eligible participants whose voluntary actions directly caused a freeze. The company offered the same percentage for funds successfully recovered through an eligible participant’s efforts.
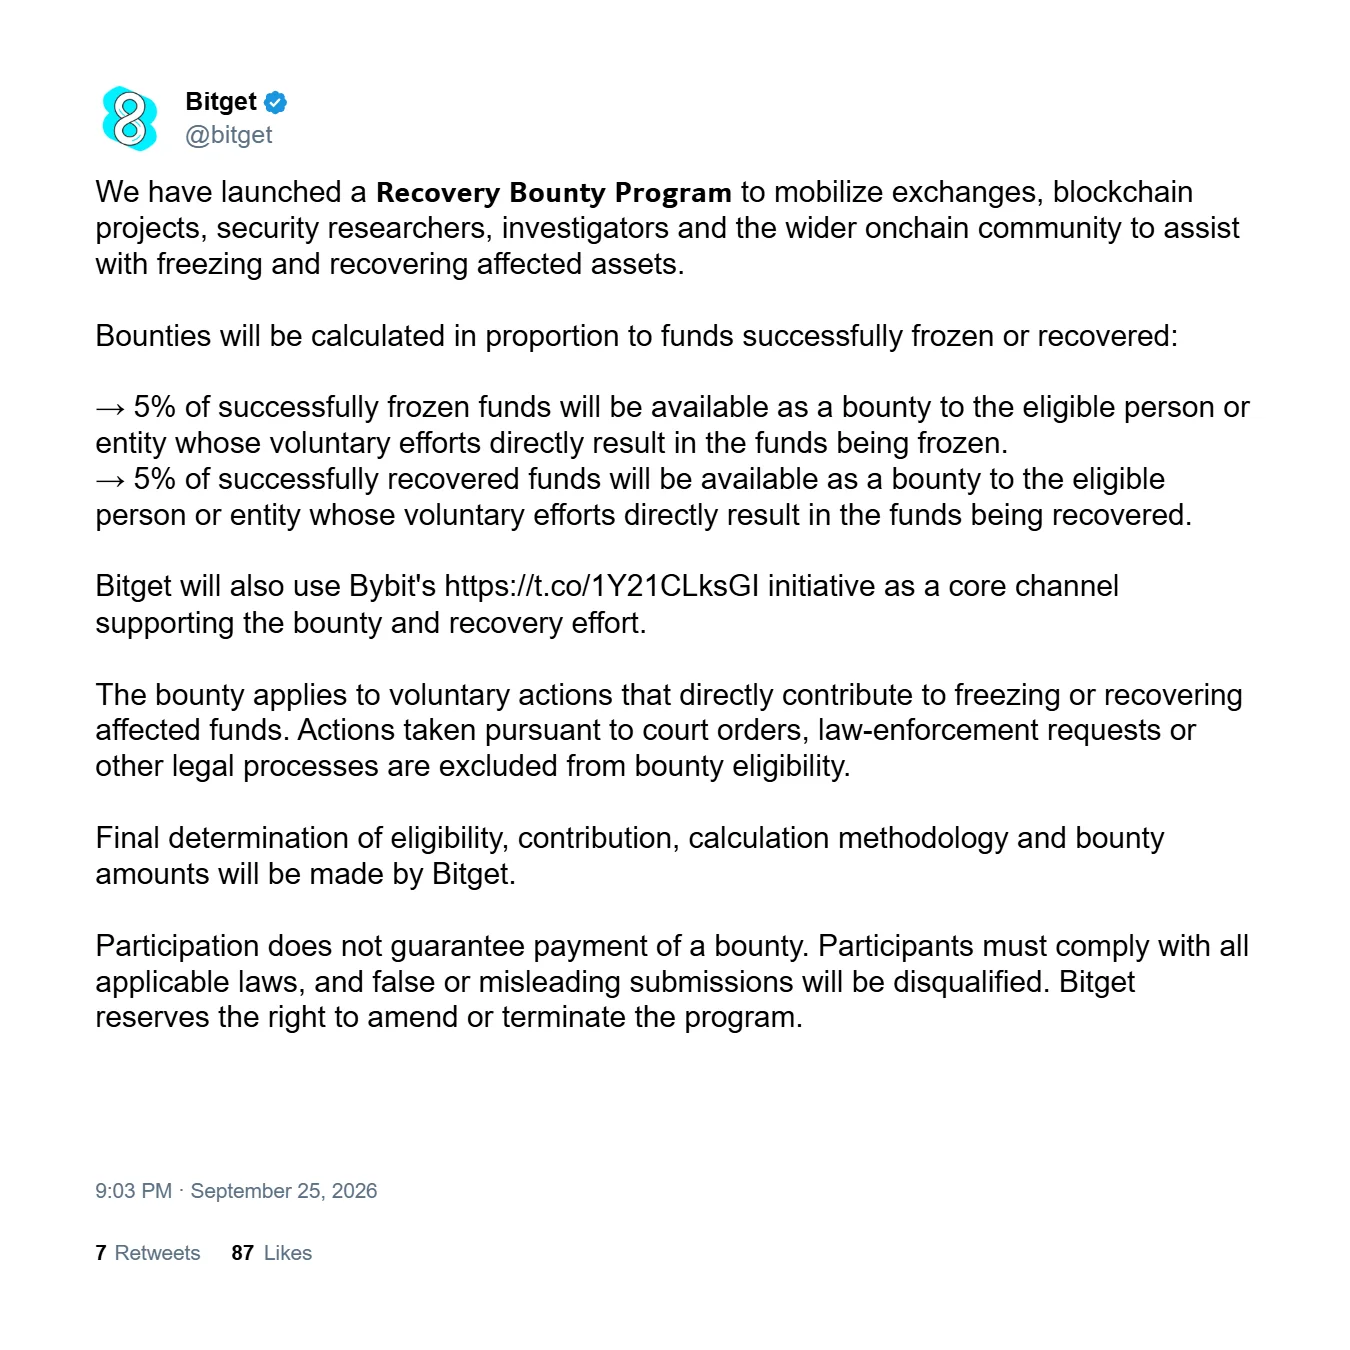
Under that structure, $1 million successfully frozen or recovered could correspond to a $50,000 bounty, subject to Bitget’s determination of eligibility, contribution and calculation methodology.
Bitget said it would use Bybit’s LazarusBounty initiative as a core recovery channel. Court-ordered actions, law-enforcement requests and other legal processes are excluded from bounty eligibility. Participation does not guarantee payment, false or misleading submissions can be disqualified, and Bitget said it may amend or end the program.
The exchange also opened live tracing tools to blockchain projects, security teams and other participants, including a fund-tracing dashboard, a recovery-reporting portal and a real-time attacker-address API. Bitget said those tools would be updated as stolen funds moved and new addresses were identified.
Protection Fund and Investigation Remain Active
Bitget said its User Protection Fund held more than $464 million and could cover the loss. The stated fund size exceeded the revised incident value by approximately $76.5 million, equivalent to about 1.20 times the confirmed amount. Chen said the fund “covers the loss.”
Bitget’s trading volume was also reported at $0 during the incident period, although that figure conflicted with Bitget’s earlier statement that trading continued while withdrawals were suspended.
Bitget said, “Our investigation and tracing efforts remain ongoing,” and added that confirmed figures “may be updated as additional transactions are classified and traced.” The exchange said future updates would cover the investigation, asset recovery, withdrawal restoration and the User Protection Fund.
This article has been refined and enhanced by ChatGPT.


